Links sent in Messenger on facebook.com opened in a new tab without rel="noopener". The opened page could quietly swap the Facebook tab for any address, for example a fake login screen. Reported to Facebook the same day, fixed the next day.
// the research was done privately in 2020, before UIES was founded; published here by its author
When a site opens a link in a new tab (target="_blank") without rel="noopener", the new page gets a reference to the tab it came from (window.opener). Through it, the new page can change the address of the original tab. The user is looking at the new tab, so the switch in the background goes unnoticed.
Links sent in a Messenger chat on facebook.com (web version) opened in a new tab and kept access to the Facebook tab. To show it, I put a test page on a temporary domain and sent its link in a chat. After the click, the test page used window.opener to send the Facebook tab to a harmless address, onet.pl.
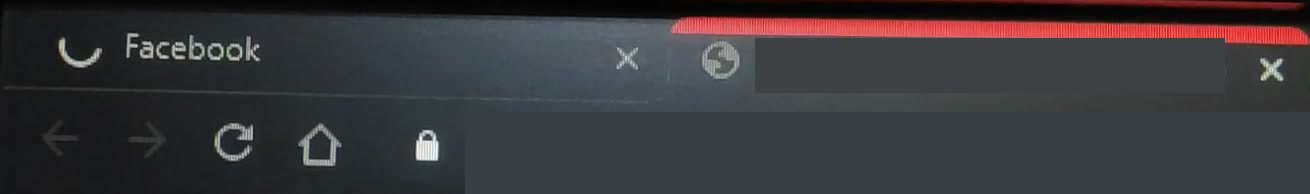
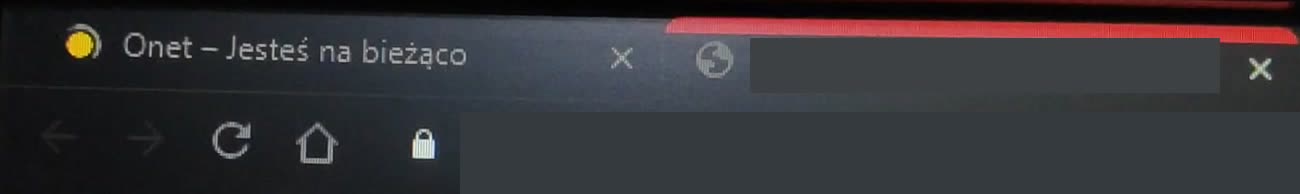
// frames from a phone video of the screen, November 2020; the test page address is masked
The proof of concept only redirected to a news site. A real attacker would do this instead:
This scenario is described, not carried out. The proof of concept used only a harmless redirect.
rel="noopener noreferrer" to links opened in a new tab.rel="noopener noreferrer" to every link with target="_blank", above all to links that users can post (comments, chat, profiles).noopener to window.open().Cross-Origin-Opener-Policy header, which cuts the link between your page and windows from other origins.target="_blank" as noopener by default, but older browsers and embedded web views may not. Setting the attribute explicitly costs nothing.